AI Governance

A new Scytale module that discovers every AI agent and tool in an organization, shows what each one can reach, and gives security teams one place to govern them.

Company
Scytale
Role
Sole product designer
Platform
B2B SaaS, web
Status
In development
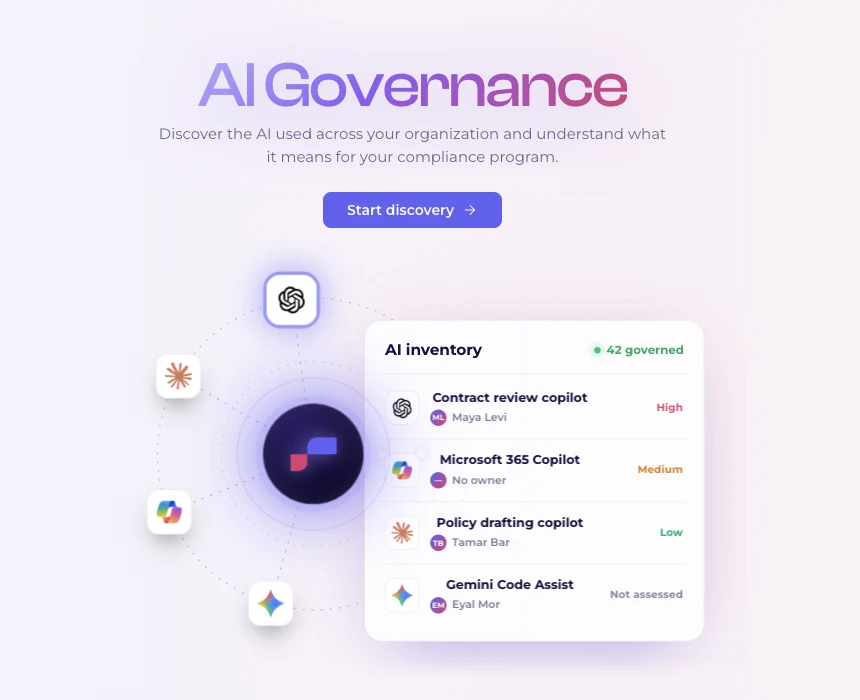
AI Governance start screen

The problem

  • Most organizations have no idea how many AI agents they run.
  • Agents are created by teams, employees and inside SaaS tools, with no intake process.
  • Little visibility into what each agent does and what data it can reach.
88.4%

of organizations had at least one agent related security breach in the past 12 months.
The research

  • We distilled the goal and the requirements together with product.
  • Interviews with compliance and security leaders.
  • The key finding: users don't need another list of AI tools. They need to know which AI puts them at risk.
  • That's why we built the whole solution around risk.
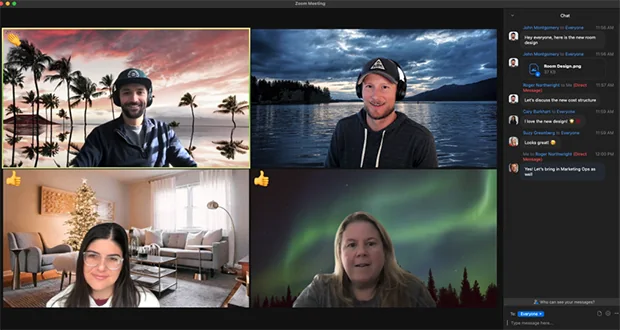
Remote interview session with four participants

The user journey

From the first scan to a decision on every agent.
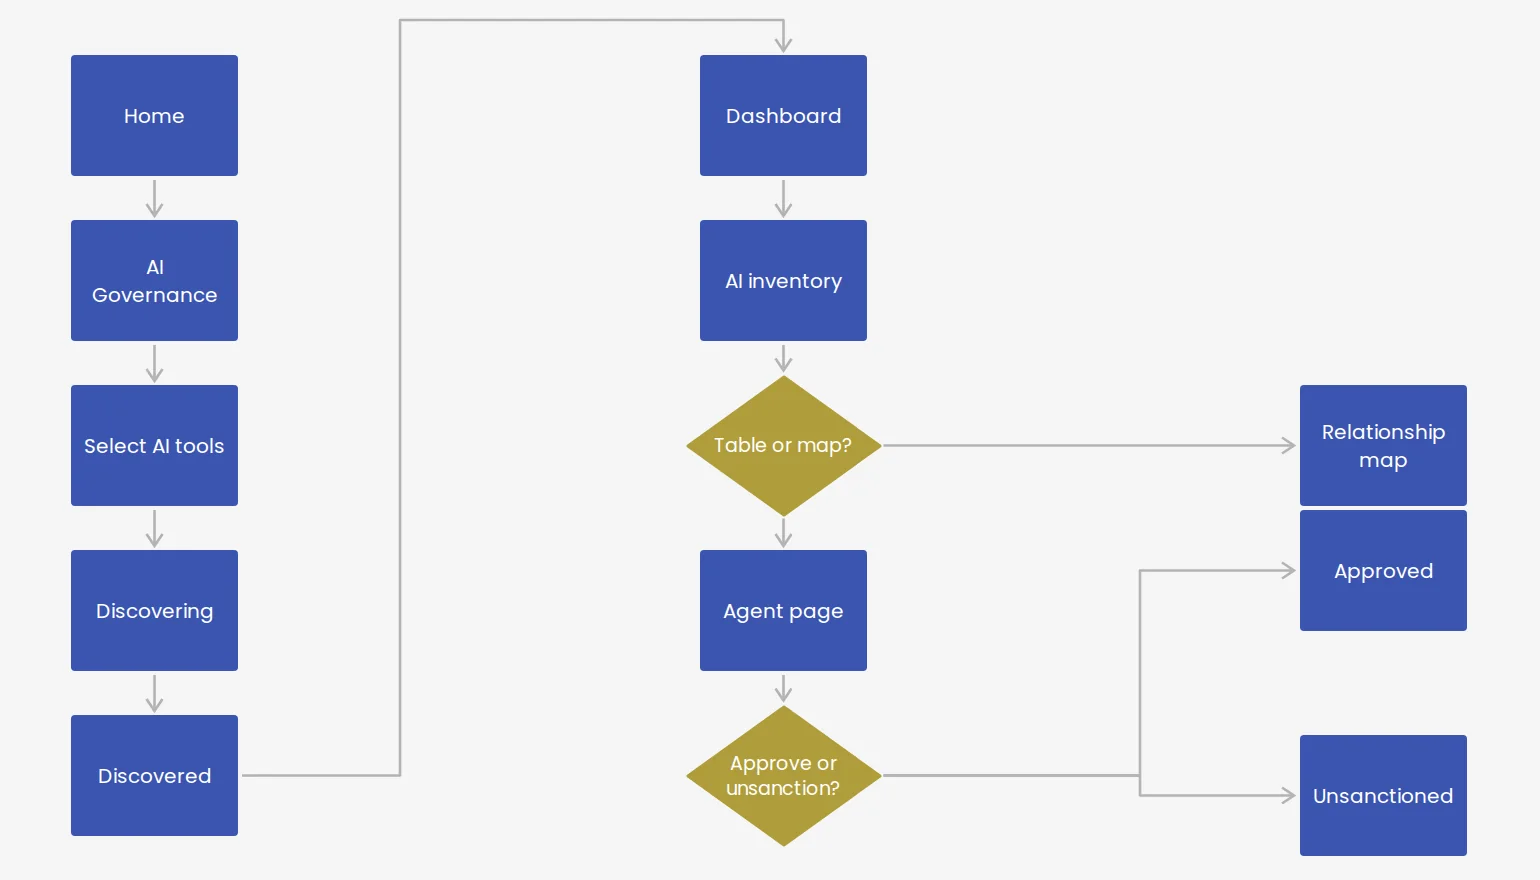
User journey from discovery to approving or unsanctioning an agent

Solution 1

One clear starting point

Problem
Most companies have no idea how much AI is running across their teams.
Solution
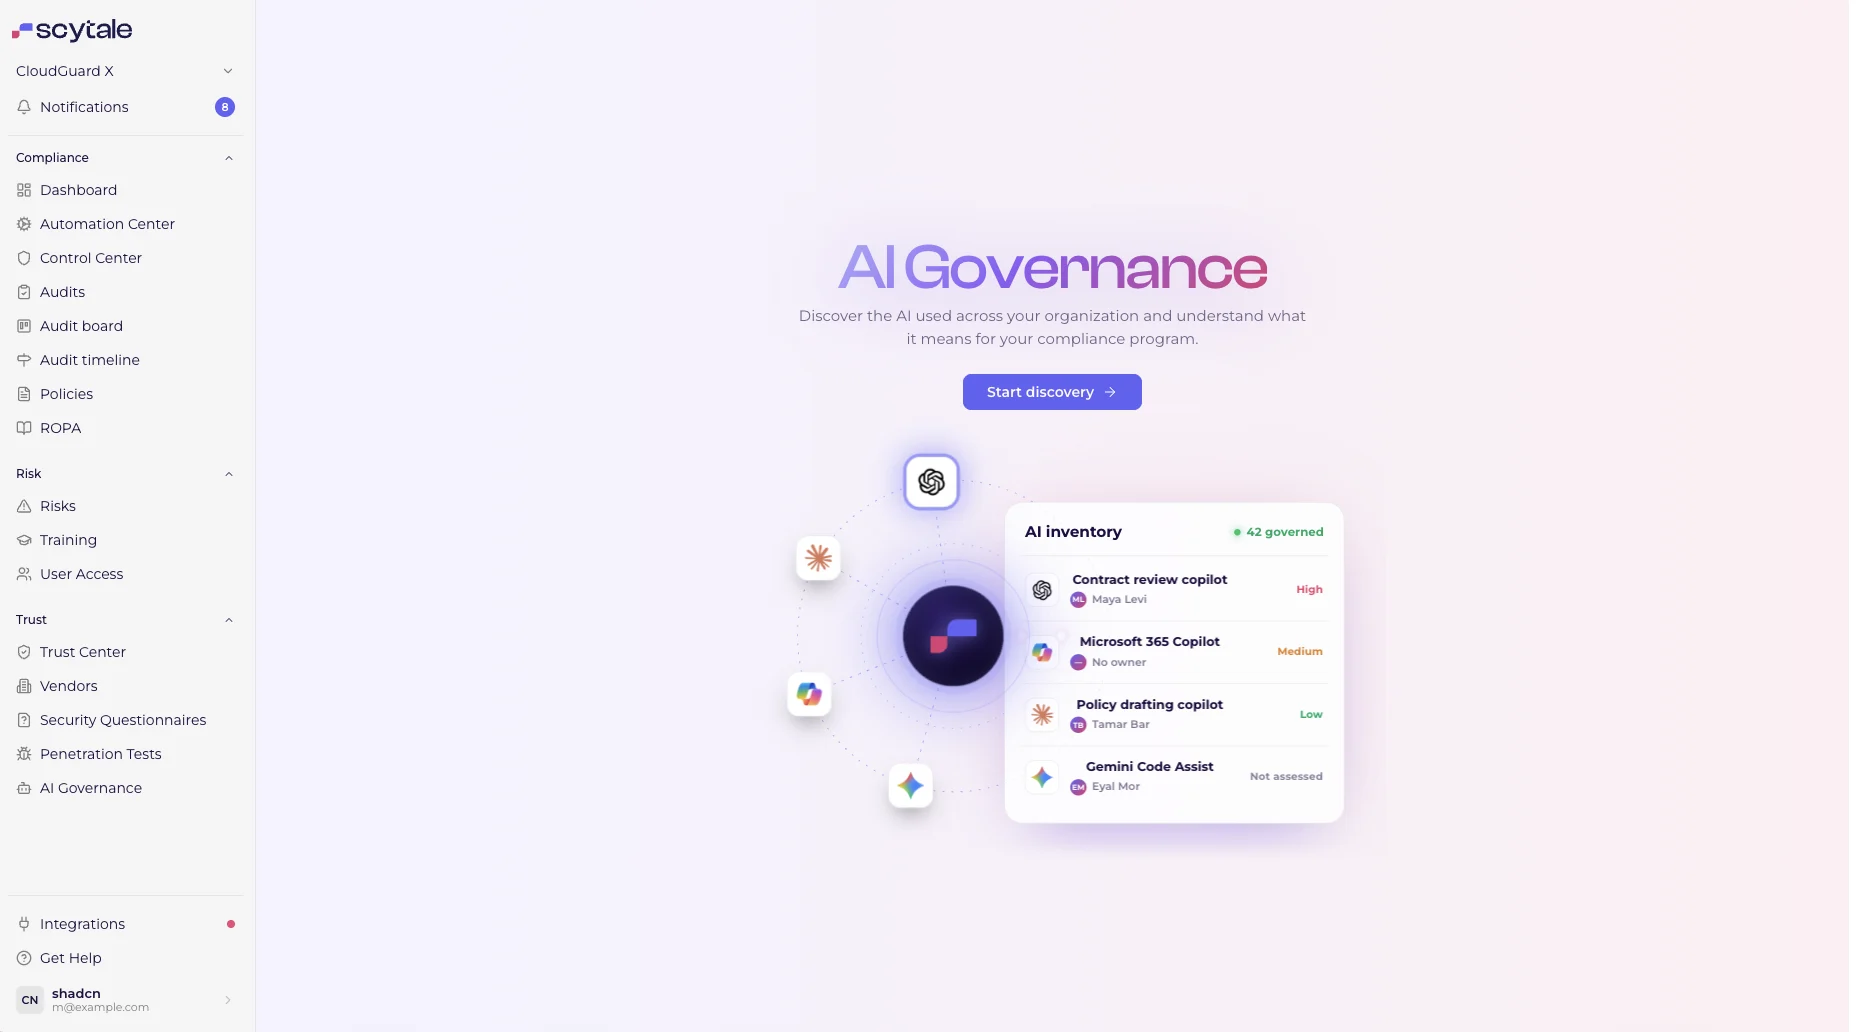
The module opens with one clear call to action: start discovery, and Scytale finds the AI for you.
AI Governance start screen

Solution 2

Connect only what you use

Problem
Every AI provider holds a different piece of the picture.
Solution
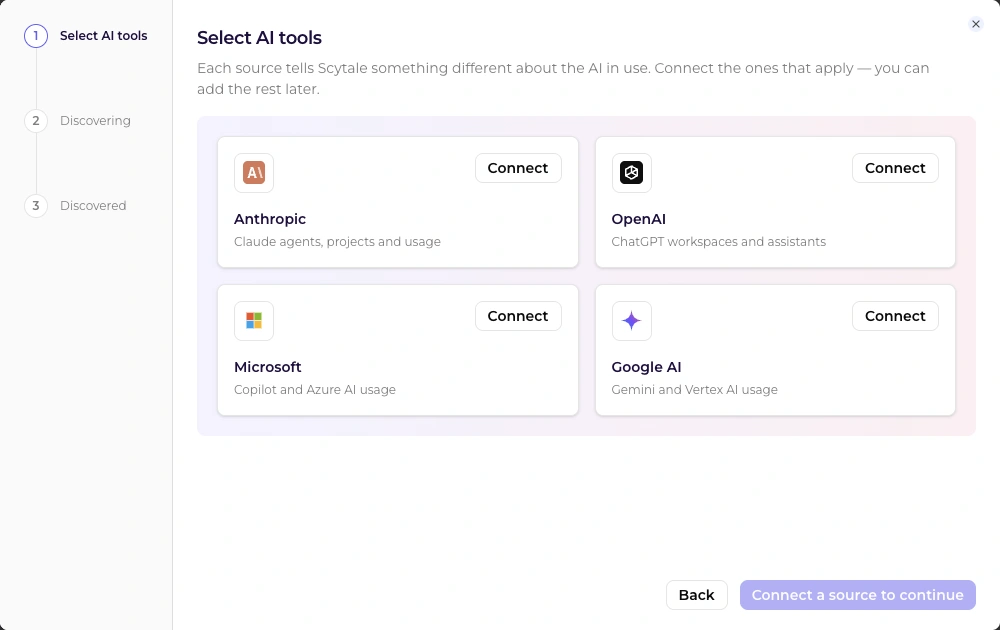
Users connect only the sources they actually use, and can add the rest later, so getting started takes minutes.
Select AI tools step

Solution 3

Proof that the scan worked

Problem
After connecting, users need to trust the results.
Solution
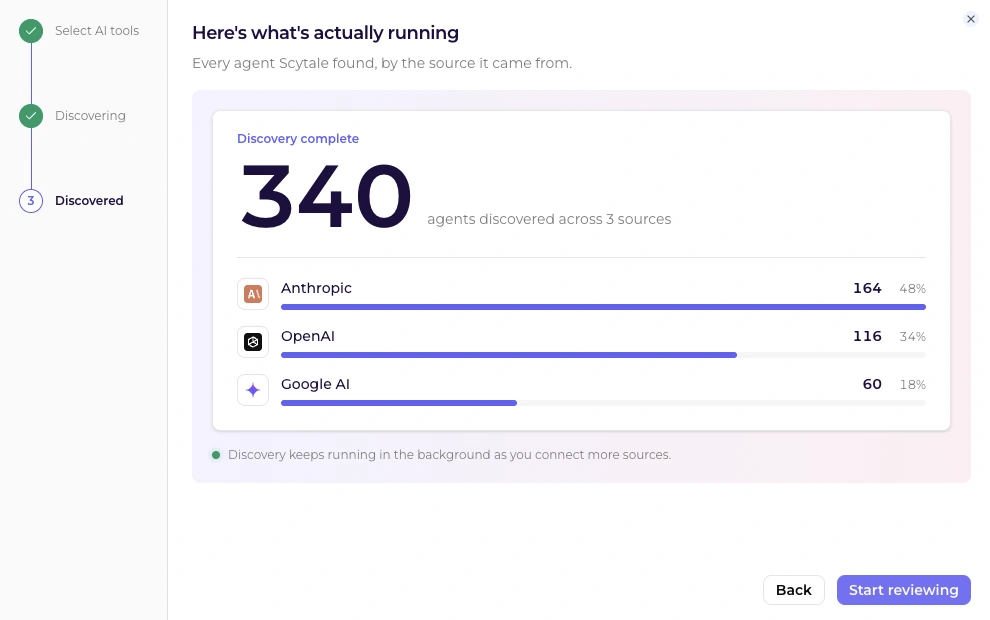
The results screen shows how many agents were found, and exactly which source each one came from.
Discovery results

Solution 4

Know where to look first

Problem
With hundreds of agents, users don't know where to focus.
Solution
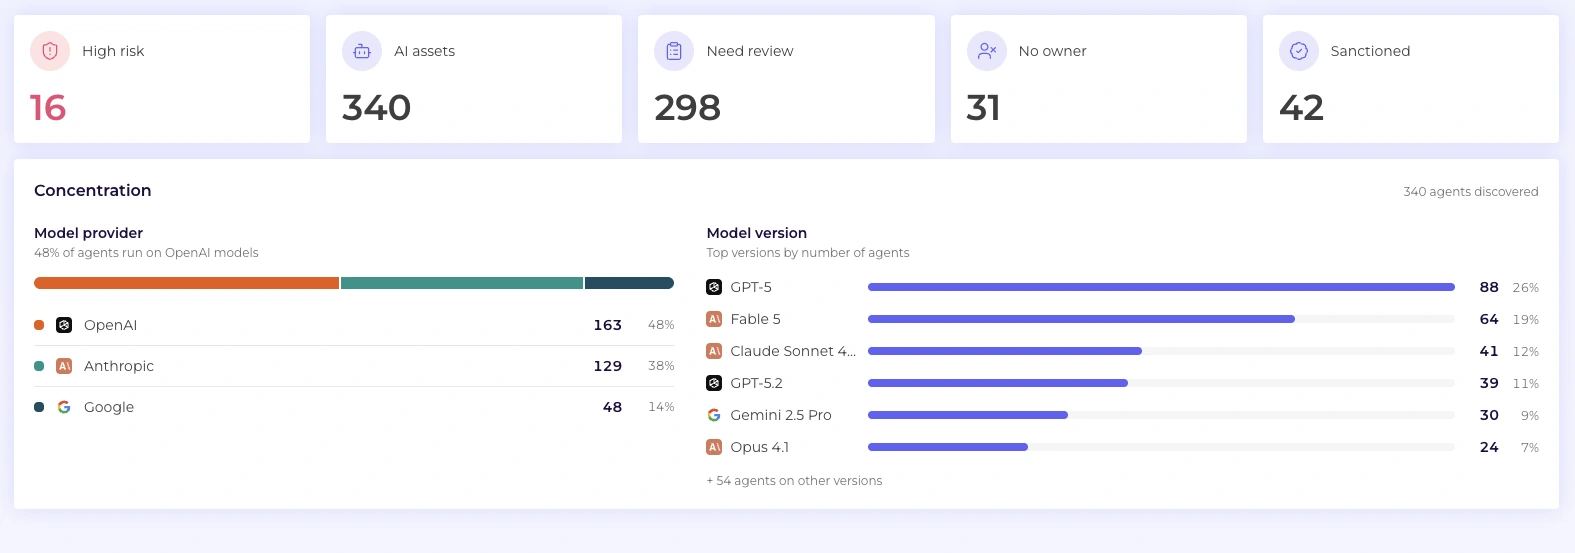
Summary cards surface high risk, need review and no owner, and the concentration view shows which models the company relies on.
AI Governance dashboard

Solution 5

An inventory built around risk

Problem
Customers have hundreds of AI assets.
Solution
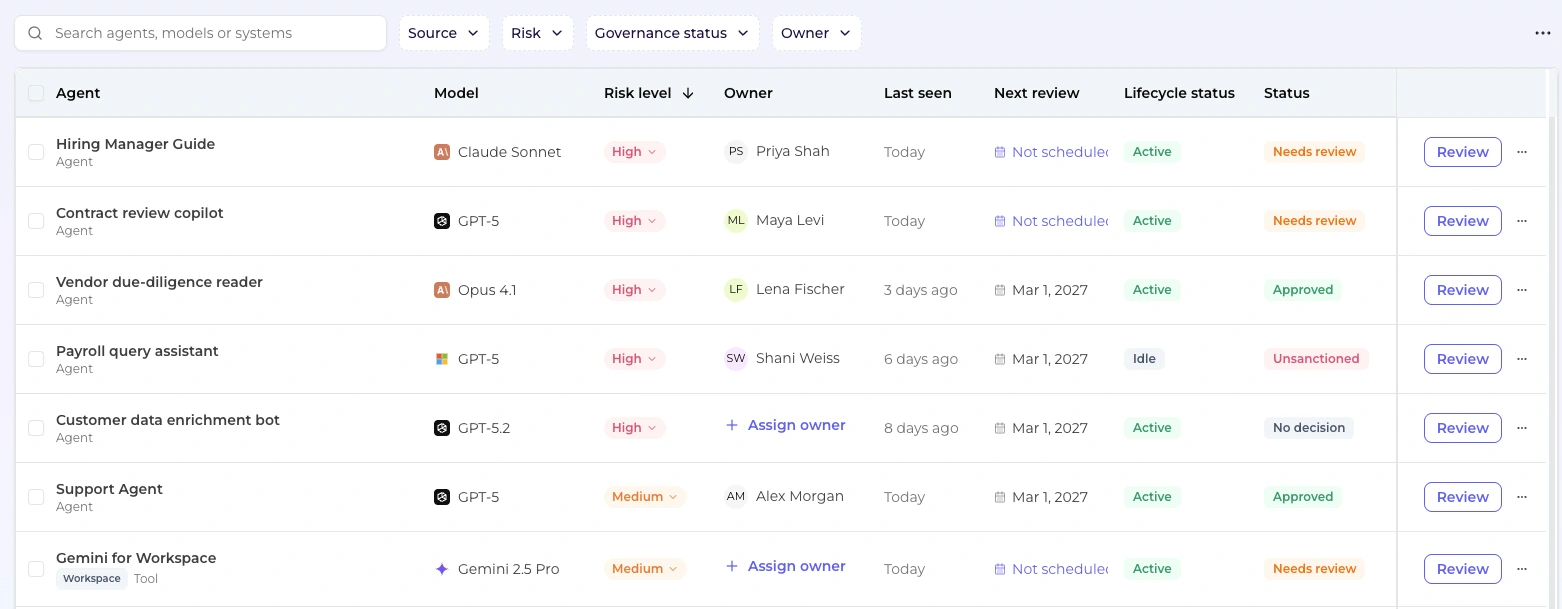
The inventory puts risk first: risk, owner and review status in one table, with filters for source, risk, status and owner.
AI inventory table

Solution 6

A full page for every agent

Problem
A drawer was too tight to explain what an agent decides, reaches and runs as.
Solution
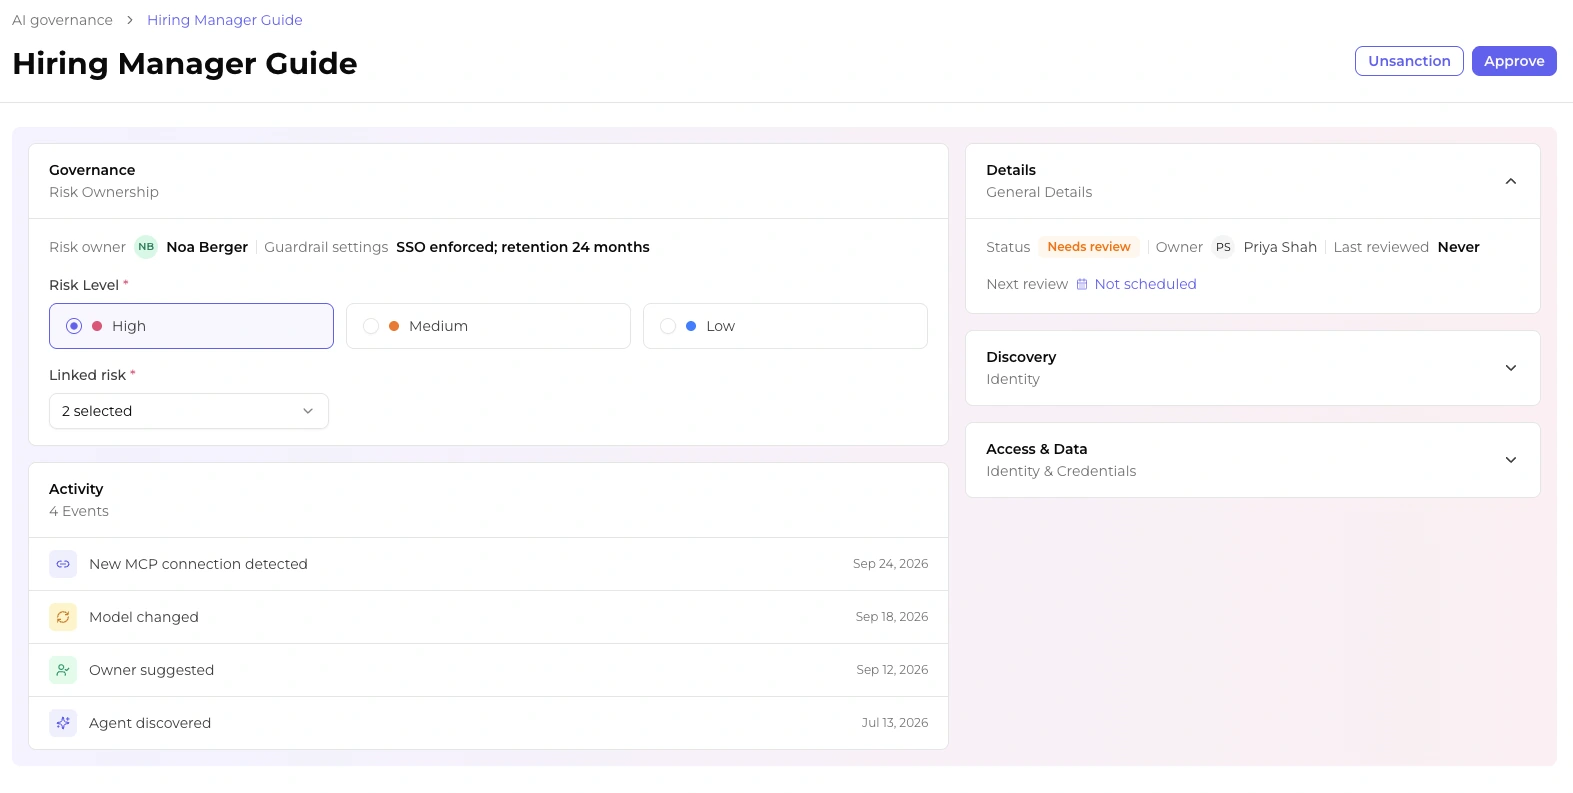
Each agent opens as a full page: risk, ownership and activity in one view, with a clear approve or unsanction decision.
Agent page

Solution 7

Risk comes from connections

Problem
Looking at one tool at a time hides how risk travels between systems.
Solution
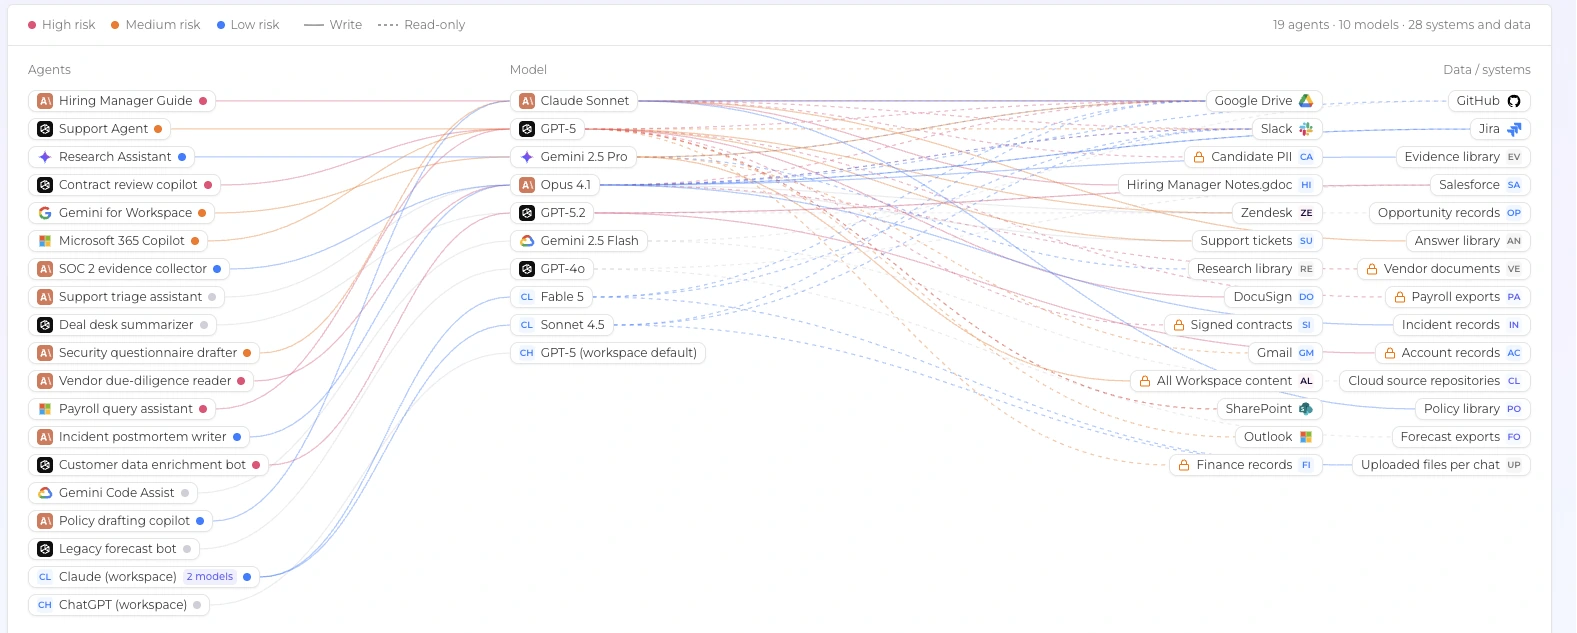
The relationship map shows how every agent, model and data source connect, colored by risk level, with write and read only access marked.
Relationship map